
Networking Services
DNS - Domain Name System
Section titled “DNS - Domain Name System”DNS is a globally distributed service that translates human-readable domain names (like example.com) into IP addresses (like 93.184.216.34). Without DNS, you’d need to memorize IP addresses to browse the web.
Why DNS Matters
Section titled “Why DNS Matters”- User-friendly - you type
github.cominstead of140.82.121.4 - Abstraction - an organization can move servers, change IPs, and users never notice (just update the DNS record)
- Load balancing - one domain can resolve to multiple IPs (DNS round robin), distributing traffic across servers
- Email routing - MX records tell the internet which mail server handles
@yourdomain.com - CDN delivery - DNS can return the nearest edge server based on the user’s location (GeoDNS)
- Security - DNSSEC adds cryptographic signatures to DNS responses, preventing spoofing and cache poisoning
DNS Server Types
Section titled “DNS Server Types”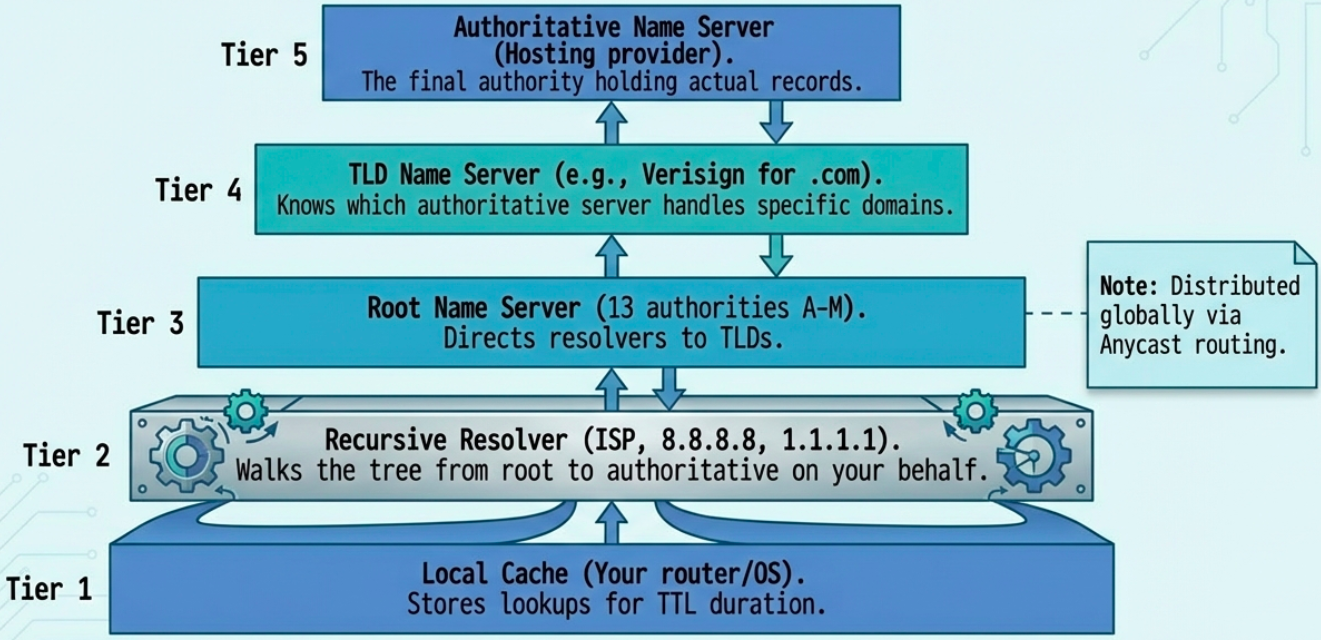
There are 5 types of DNS servers, each with a specific role in the resolution chain:
| Server Type | Role | Example |
|---|---|---|
| Caching name server | Stores previous lookups for TTL duration. Speeds up repeat queries. | Your router, local DNS cache |
| Recursive resolver | Does the full lookup on your behalf - walks the tree from root to authoritative | ISP DNS, 8.8.8.8 (Google), 1.1.1.1 (Cloudflare) |
| Root name server | First step - directs resolver to the correct TLD server. 13 root authorities (A through M), distributed globally via Anycast | a.root-servers.net through m.root-servers.net |
| TLD name server | Manages a top-level domain (.com, .org, .uk, etc.) and knows which authoritative server handles each domain in that TLD | Verisign operates .com and .net TLD servers |
| Authoritative name server | The final authority - holds the actual DNS records (A, MX, CNAME, etc.) for a specific domain | Your hosting provider’s nameservers |
The Full DNS Resolution Process
Section titled “The Full DNS Resolution Process”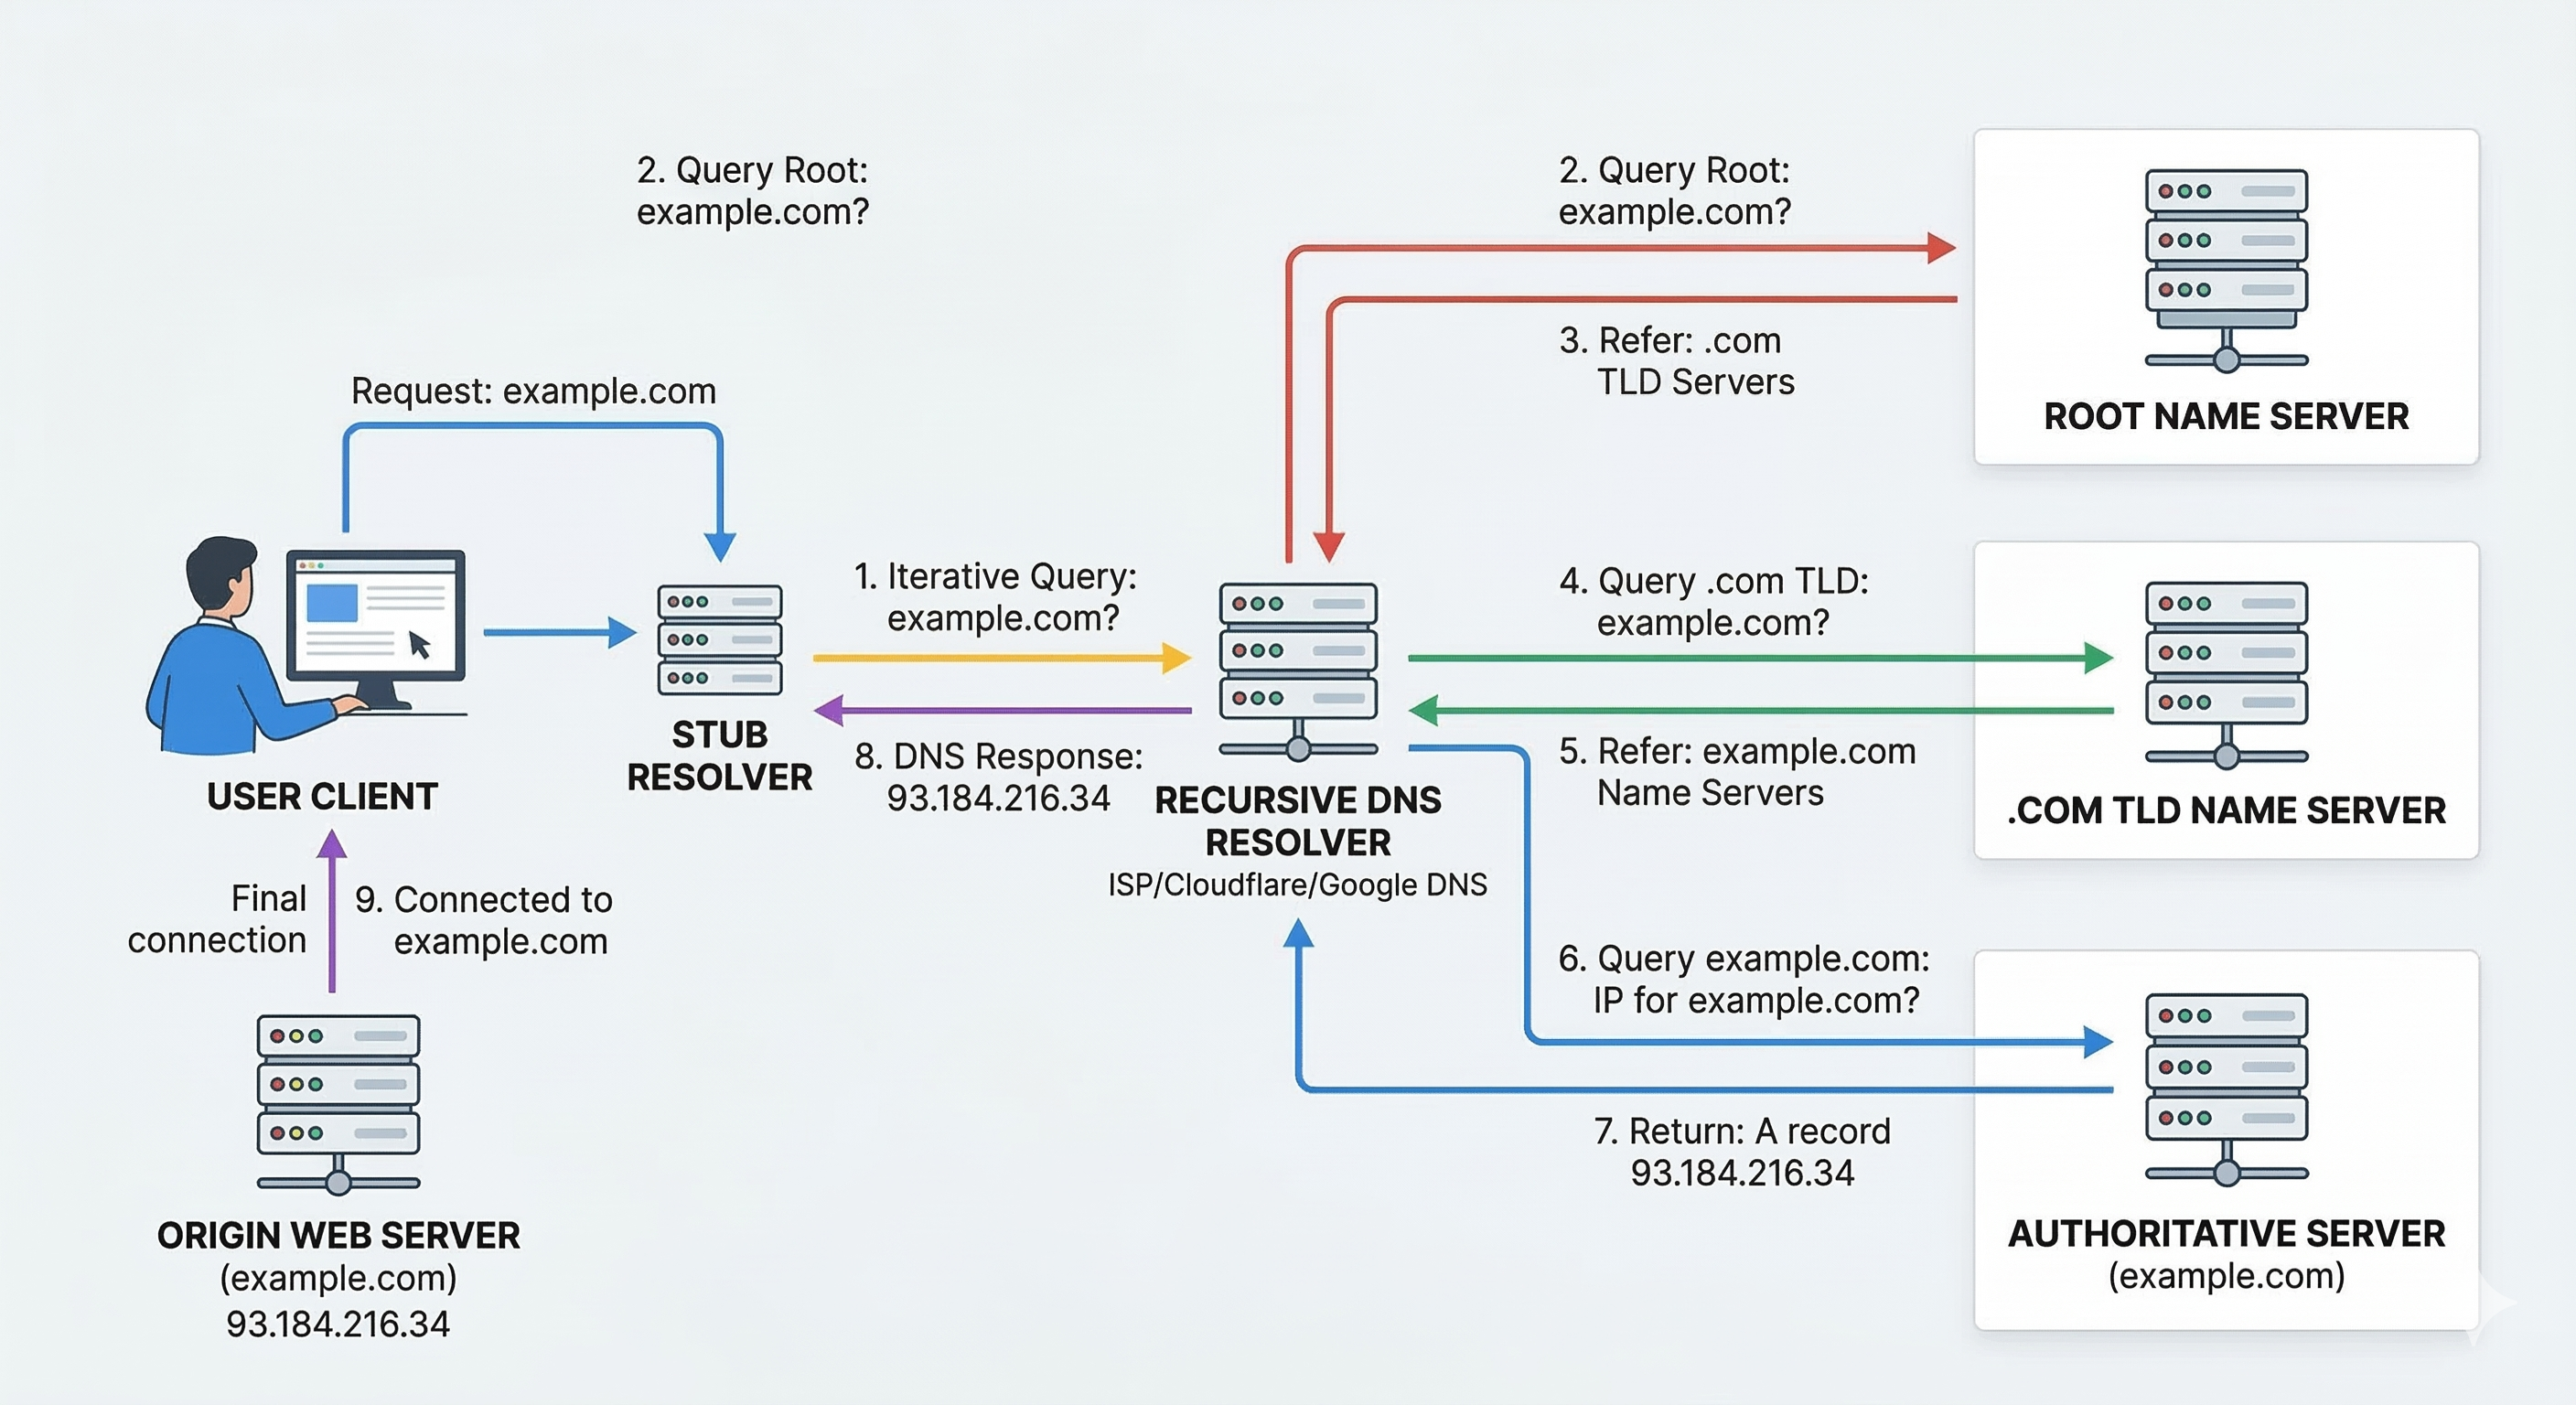
When you type www.example.com in your browser, here’s what happens:
- Local hosts file - OS checks
/etc/hosts(Linux/Mac) orC:\Windows\System32\drivers\etc\hosts(Windows) first. If there’s a match, resolution stops here. - Local DNS cache - OS checks its own cache of recent lookups
- Recursive resolver - query goes to your configured DNS resolver (usually your ISP’s, or
8.8.8.8/1.1.1.1) - Root server - resolver asks a root server “who handles
.com?” - TLD server - root directs to
.comTLD server. Resolver asks “who handlesexample.com?” - Authoritative server - TLD directs to
example.com’s authoritative nameserver. Resolver asks “what’s the IP forwww.example.com?” - IP returned - authoritative server responds with the IP address
- Caching - resolver caches the result for the record’s TTL (Time To Live) duration
- Response to client - resolver sends the IP back to your browser
TTL (Time To Live) is a value in seconds set by the domain owner. It tells resolvers how long to cache a record before re-querying. Low TTL (60-300s) = faster propagation of changes. High TTL (3600-86400s) = less DNS traffic but slower change propagation.
Recursive and iterative queries
Section titled “Recursive and iterative queries”Two kinds of query are involved in one lookup.
| Query | Between | What it asks |
|---|---|---|
| Recursive | Client and its resolver | ”Return the final answer, or an error. Do the work for me.” |
| Iterative | Resolver and each name server | ”Answer if you can, otherwise tell me who to ask next.” |
The client sends a single recursive query. The resolver then walks the hierarchy with iterative queries: the root server answers with a referral to the .com servers, the TLD server answers with a referral to the domain’s authoritative servers, and the authoritative server returns the record. dig +trace plays the resolver’s role from your own machine.
# Ask a root server without requesting recursion: it returns a referral, not an answerdig +norecurse @a.root-servers.net www.example.com
# The AUTHORITY section lists the NS records of the .com servers to ask next
Caching and negative caching
Section titled “Caching and negative caching”Every step of that walk is cached, at the browser, at the operating system, and at the resolver. Resolvers keep the NS records for TLDs, so they almost never contact a root server and a repeat lookup completes in about the cost of a local call.
Failures are cached too. If a name does not exist, the resolver stores the NXDOMAIN answer for the negative-caching time, taken from the zone’s SOA record. A record you have just created can therefore look missing for a few minutes on resolvers that asked first.
# See the zone's SOA, which includes the negative-caching time (last field)dig SOA example.com +short
# Clear the local cache on Linux with systemd-resolvedresolvectl flush-caches
# Clear it on macOSsudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder
Before a planned address change, lower the record’s TTL at least one old-TTL period in advance. Resolvers that cached the record under the old TTL keep serving it until that time runs out, regardless of what you set afterwards.
DNS and UDP
Section titled “DNS and UDP”DNS primarily uses UDP (port 53) instead of TCP. Why?
- A DNS query + response usually fits in a single UDP datagram - no handshake overhead needed
- No connection setup/teardown = far fewer packets. A recursive lookup via TCP requires ~44 packets minimum; via UDP, only ~8
- DNS implements its own retry logic at the application layer - if no response arrives, the resolver simply asks again. No need for TCP’s reliability guarantees
DNS Record Types
Section titled “DNS Record Types”| Record Type | Purpose | Example |
|---|---|---|
| A | Maps domain to IPv4 address | example.com -> 93.184.216.34 |
| AAAA | Maps domain to IPv6 address | example.com -> 2606:2800:220:1:... |
| CNAME | Alias - points one name to another | www.example.com -> example.com |
| MX | Mail server for the domain (with priority) | example.com -> mail.example.com (priority 10) |
| NS | Authoritative nameservers for the zone | example.com -> ns1.example.com |
| SOA | Start of Authority - zone metadata (primary NS, admin email, serial, refresh intervals) | One per zone |
| PTR | Reverse lookup - IP to domain name | 34.216.184.93.in-addr.arpa -> example.com |
| TXT | Arbitrary text - used for SPF, DKIM, domain verification | v=spf1 include:_spf.google.com ~all |
| SRV | Service location (host + port for specific services) | _sip._tcp.example.com -> sipserver.example.com:5060 |
A single domain can have multiple A records - this is DNS round robin, a basic form of load balancing where each query returns the records in a different order, distributing traffic across servers.
DNS message format
Section titled “DNS message format”Queries and responses share one layout: a 12-byte header followed by four sections.
+----------------------------------------+| Header ID, flags, section counts || Question name and type being asked || Answer the requested records || Authority NS records pointing deeper || Additional extra records (glue) |+----------------------------------------+The ID is a 16-bit number that the resolver copies into the reply so it can match answers to outstanding queries. Resolvers also randomize the source port, which makes a forged reply much harder to guess. Four counts in the header say how many entries each section holds. The Authority section carries NS records for the next servers to ask, and Additional carries their IP addresses (glue records) so the resolver does not need a second lookup.
dig prints the header flags and counts at the top of its output.
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 41873;; flags: qr rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1| Flag | Meaning |
|---|---|
qr | This message is a response, not a query |
rd | Recursion desired: the client asked the server to resolve fully |
ra | Recursion available: the server is willing to |
aa | Authoritative answer: sent by a server that owns the zone, not from cache |
tc | Truncated: the reply did not fit in a UDP datagram, so retry over TCP |
The status value in the header is the quickest read on what went wrong.
| Status | Meaning |
|---|---|
NOERROR | The query succeeded. An empty answer means the name exists but has no record of that type |
NXDOMAIN | The name does not exist |
SERVFAIL | The server could not complete the lookup. A failed DNSSEC validation is a common cause |
REFUSED | The server declined to answer, usually due to an access control rule |
Anatomy of a Domain Name
Section titled “Anatomy of a Domain Name”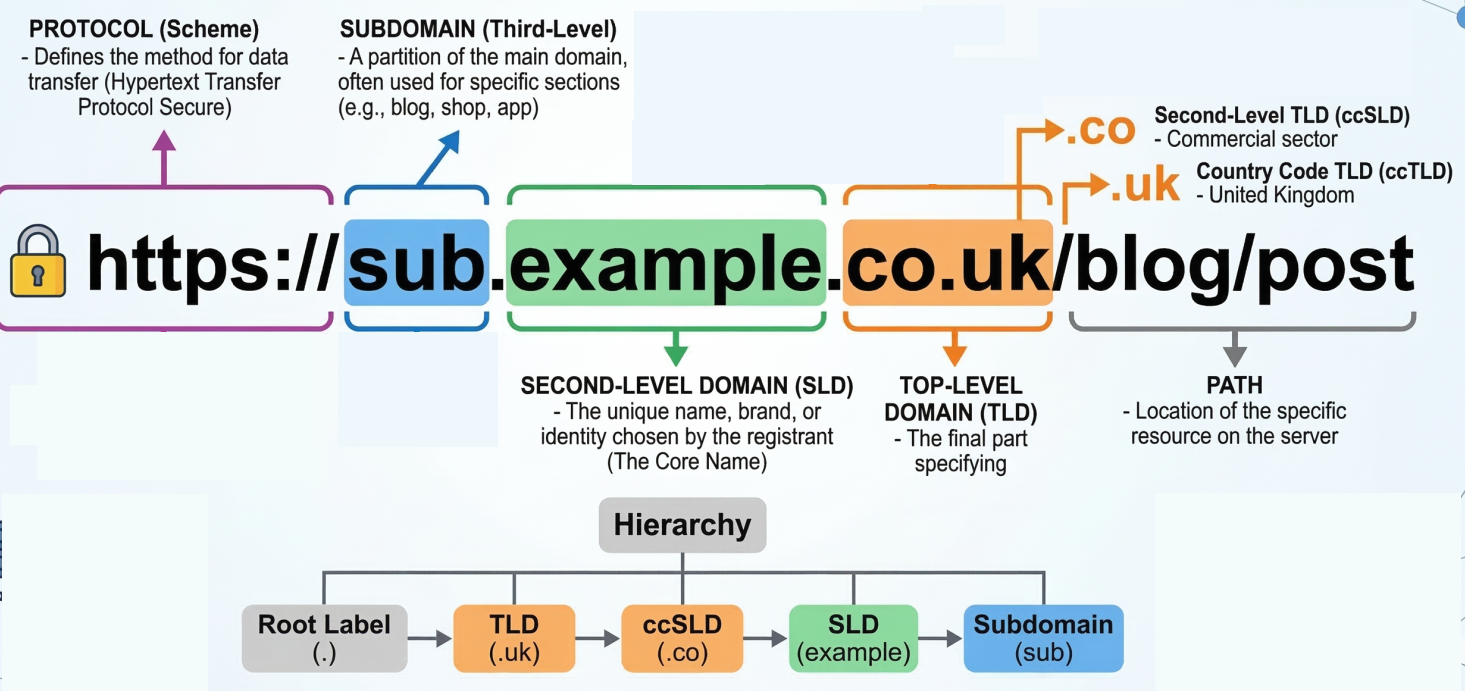
https://mail.example.com:443/inbox?sort=date&filter=unread ───┬── ──┬─ ───┬──── ─┬─ ─┬─ ──┬── ─────────┬──────────Protocol Sub Domain TLD Port Path Query Parameters domain| Component | Description |
|---|---|
| TLD (Top-Level Domain) | .com, .org, .net, country codes like .uk, .de. Managed by ICANN. |
| Domain | The registered name (example). You buy this from a registrar. |
| Subdomain | Optional prefix (mail, www, api). Free to create if you own the domain. |
| FQDN (Fully Qualified Domain Name) | The complete path: mail.example.com. (note the trailing dot - root zone) |
Technical limits: Max 127 levels deep, max 63 characters per label, max 255 characters total for an FQDN.
DNS Zones and Zone Files
Section titled “DNS Zones and Zone Files”A DNS zone is a portion of the DNS namespace managed by a specific organization. Zones let administrators split large domains into manageable chunks.
- Zone file - a plain-text file on a DNS server containing all records for that zone. Starts with an SOA record (admin contact, serial number, refresh intervals) followed by NS, A, MX, and other records.
- Zone transfer - copying zone data from a primary DNS server to secondary servers for redundancy (uses TCP, port 53)
- Reverse lookup zone - maps IPs back to domain names using PTR records (uses the special
in-addr.arpadomain for IPv4)
DHCP - Dynamic Host Configuration Protocol
Section titled “DHCP - Dynamic Host Configuration Protocol”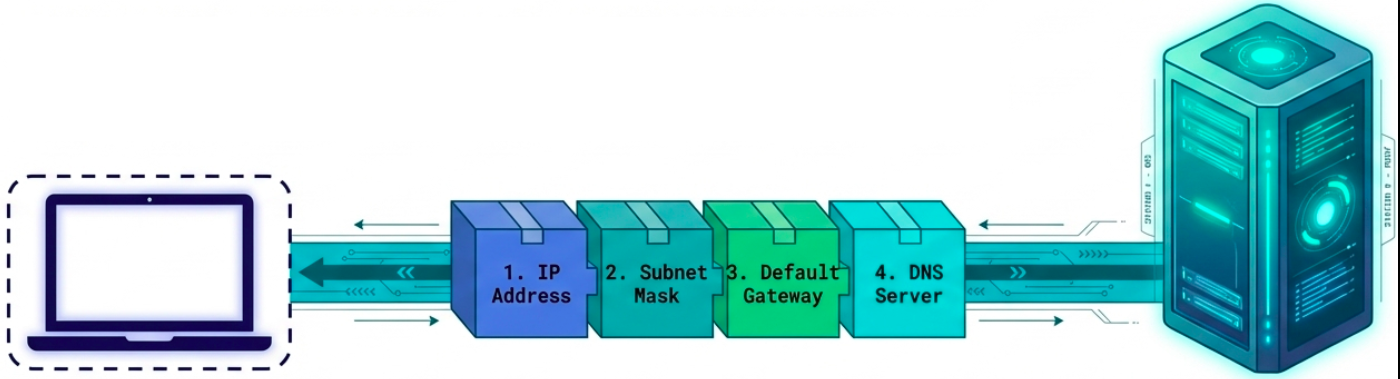
DHCP automates network configuration for client devices. Instead of manually setting IP address, subnet mask, gateway, and DNS server on every device, a DHCP server hands out configurations automatically.
Every host needs 4 things to work on a network:
- IP address
- Subnet mask
- Default gateway (router)
- DNS server
DHCP configures all four in one go. Servers and network equipment typically use static IPs (you always need to know where they are). Client devices (laptops, phones) use DHCP.
DHCP Allocation Modes
Section titled “DHCP Allocation Modes”| Mode | Behavior |
|---|---|
| Dynamic | Server assigns an IP from a pool for a limited lease period. IP returns to pool when lease expires. |
| Automatic | Server assigns a permanent IP from the pool - same IP every time if possible. |
| Fixed (reservation) | Admin maps specific MAC addresses to specific IPs in a table. Guarantees a device always gets the same IP. |
The DORA Process
Section titled “The DORA Process”DHCP uses a four-step handshake called DORA: Discover, Offer, Request, Acknowledge. All communication happens over UDP - server listens on port 67, client sends from port 68.
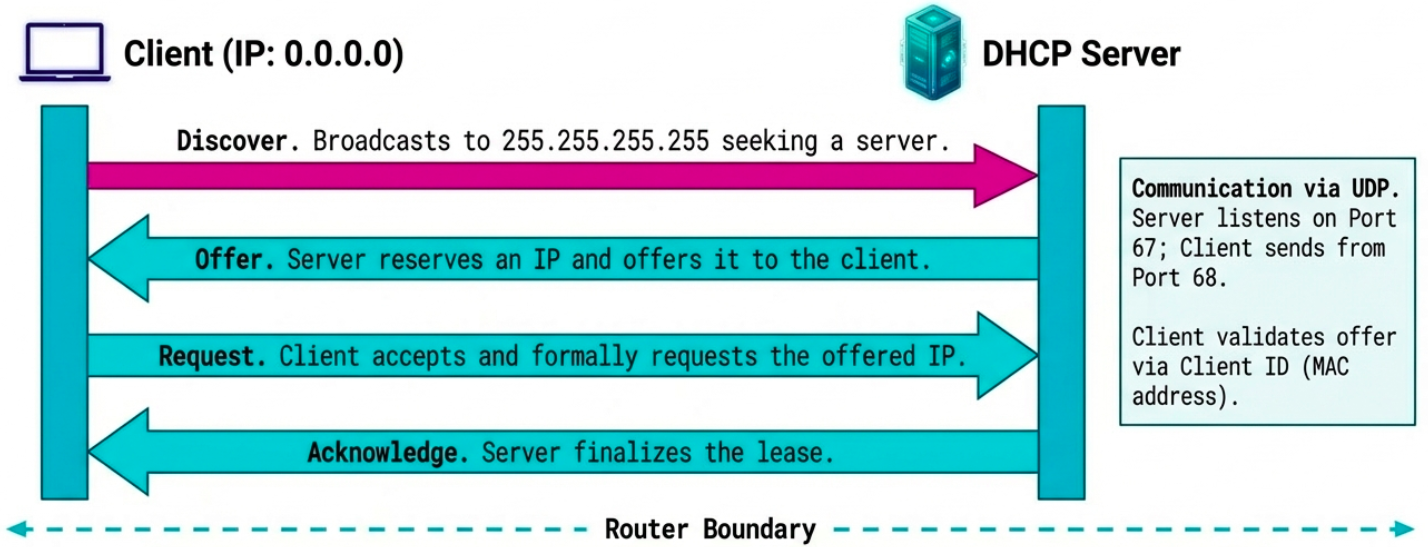
Client (no IP yet) DHCP Server | | 1. |-- DHCPDISCOVER (broadcast) -------->| "Anyone got an IP for me?" | src: 0.0.0.0:68 | (sent to 255.255.255.255:67) | dst: 255.255.255.255:67 | | | 2. |<-------- DHCPOFFER (broadcast) -----| "Here's 192.168.1.50, lease 24h" | dst: 255.255.255.255:68 | (includes subnet, gateway, DNS) | (identifies client by MAC) | | | 3. |-- DHCPREQUEST (broadcast) --------->| "I'll take that 192.168.1.50" | (also tells other DHCP servers | | to withdraw their offers) | | | 4. |<-------- DHCPACK (broadcast) -------| "Confirmed. It's yours for 24h." | | |===== Client configures interface ===|Edge cases:
- Multiple DHCP servers - client may receive multiple OFFERs; it accepts one and the others withdraw
- DHCPDECLINE - client rejects an offer if the IP conflicts with something on the network
- DHCPNACK - server withdraws the offer (client took too long to respond)
- Lease renewal - client automatically tries to renew at 50% of lease time (T1) and again at 87.5% (T2)
DHCP options
Section titled “DHCP options”The offer carries more than an address. Each extra setting is a numbered option.
| Option | Content | Used for |
|---|---|---|
| 1 | Subnet mask | Sizing the local subnet |
| 3 | Router | Default gateway |
| 6 | DNS servers | Name resolution |
| 15 | Domain name | Search suffix |
| 42 | NTP servers | Time sync |
| 51 | Lease time | How long the address is valid |
| 66 and 67 | TFTP server and boot file | PXE network boot |
| 121 | Classless static routes | Pushing extra routes to clients |
When a relay forwards a request, it writes its own interface address into the giaddr field. The server uses that address to choose the right scope (address pool) for the client’s subnet. One central server can therefore serve many VLANs, as long as each VLAN’s router has a relay configured.
A new address on a new subnet also breaks any TCP connection bound to the old one. Applications that must survive a network change need to reconnect, or use QUIC, which keeps a connection alive across an address change (see HTTP and web protocols).
# Watch the exchange on the wire (server port 67, client port 68)sudo tcpdump -i eth0 -n -vv 'udp port 67 or udp port 68'| Symptom | Likely cause | Fix |
|---|---|---|
Host has a 169.254.x.x address | No DHCP server reachable | Check the cable or VLAN, the relay on the subnet’s router, and that the server is running |
| Clients on one VLAN get nothing, others work | Relay missing on that VLAN’s gateway | Add the ip helper-address or equivalent |
| Clients get a wrong gateway or DNS | A rogue DHCP server answered first | Enable DHCP snooping on the switches |
| Addresses run out | Pool too small or lease time too long | Enlarge the scope or shorten the lease |
NAT - Network Address Translation
Section titled “NAT - Network Address Translation”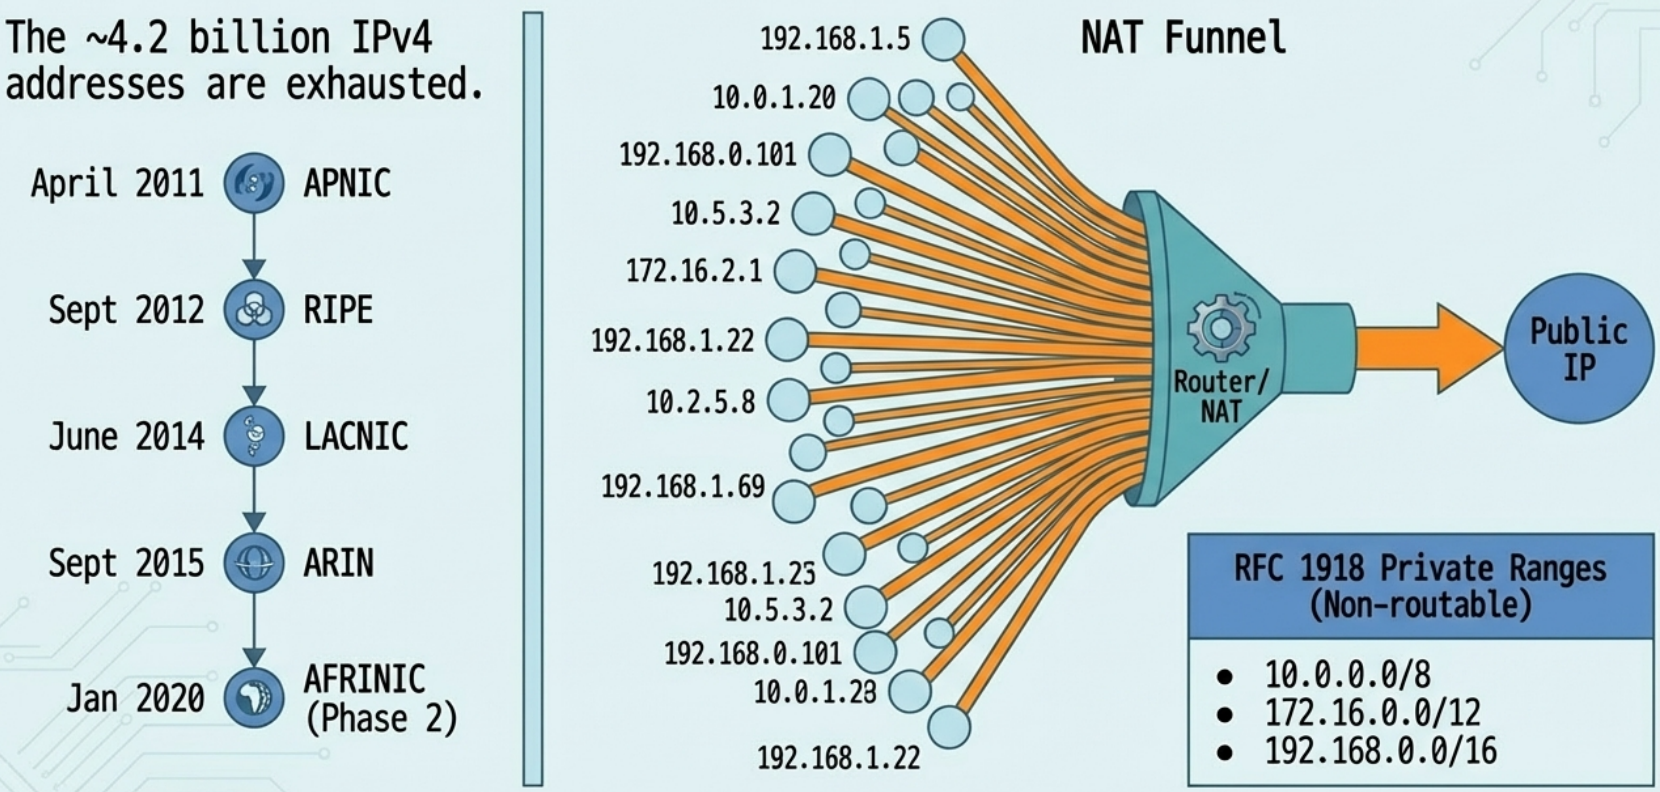
NAT allows a router/firewall to rewrite the source IP of outgoing packets so that many devices on a private network can share a single public IP address. The router remembers the mapping and rewrites return traffic back to the correct internal device.
NAT exists because of IPv4 address exhaustion - there are only ~4.2 billion IPv4 addresses, and they ran out:
| RIR | Region | Exhaustion Date |
|---|---|---|
| APNIC | Asia-Pacific | April 2011 |
| RIPE | Europe, Middle East | September 2012 |
| LACNIC | Latin America, Caribbean | June 2014 |
| ARIN | North America | September 2015 |
| AFRINIC | Africa | Phase 2: January 2020 |
RFC 1918 private address ranges (non-routable on the public internet):
10.0.0.0/8(10.0.0.0 - 10.255.255.255)172.16.0.0/12(172.16.0.0 - 172.31.255.255)192.168.0.0/16(192.168.0.0 - 192.168.255.255)
How NAT Works at the Transport Layer
Section titled “How NAT Works at the Transport Layer”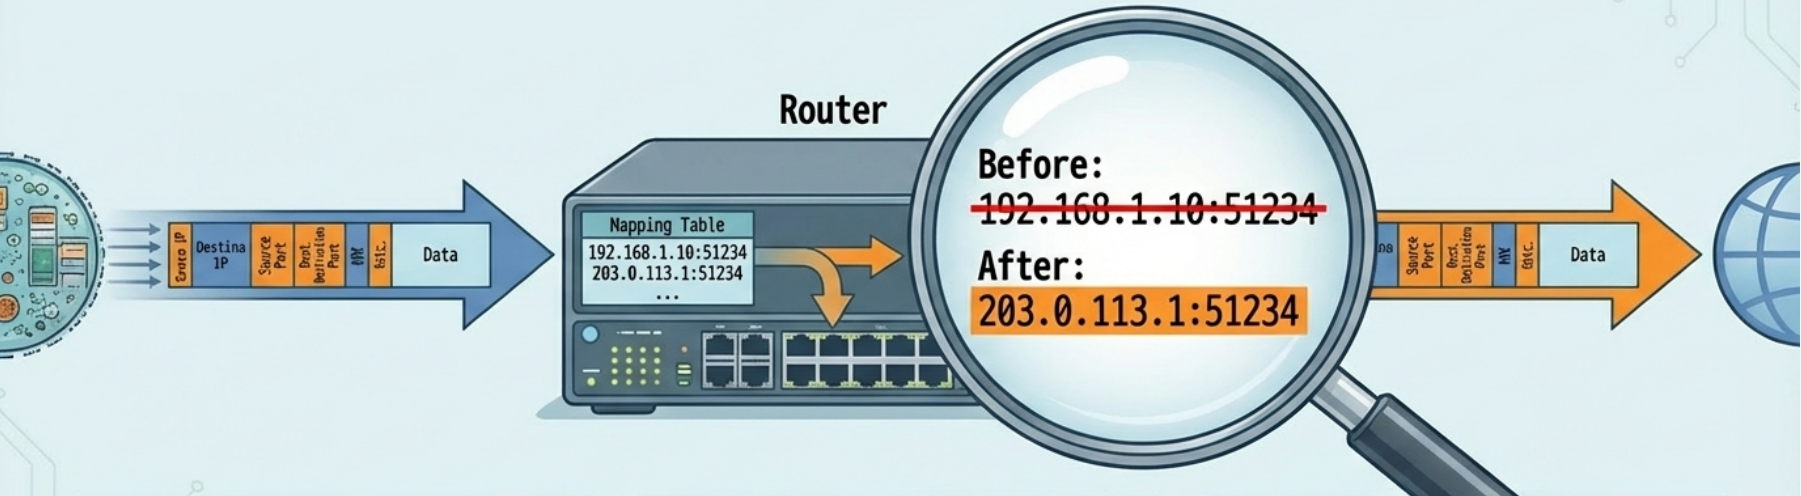
NAT doesn’t just rewrite IPs - it also tracks ports to handle many-to-one mapping:
- Port preservation - the router tries to keep the client’s original source port. If
192.168.1.10:51234sends a packet, the router maps it to203.0.113.1:51234. Return traffic to:51234gets forwarded back to the correct internal host. - Port collision - if two internal hosts pick the same ephemeral port, the router reassigns one to a random unused port
- Port forwarding - manually maps an incoming destination port to a specific internal IP:port. This is how you expose a web server behind NAT.
# Check NAT/masquerade rules on Linux (iptables)sudo iptables -t nat -L -n -v
# Set up basic NAT masqueradingsudo iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
# Port forwarding: forward external port 8080 to internal 192.168.1.100:80sudo iptables -t nat -A PREROUTING -p tcp --dport 8080 -j DNAT --to-destination 192.168.1.100:80
# nftables equivalentsudo nft add rule nat postrouting oifname "eth0" masquerade
The translation table
Section titled “The translation table”The router keeps a table that maps each internal connection to a public IP and port. The public side is the only address the internet sees.
| Direction | Source | Destination |
|---|---|---|
| Outbound, before NAT | 192.168.1.10:51234 | 198.51.100.20:443 |
| Outbound, after NAT | 203.0.113.1:40001 | 198.51.100.20:443 |
| Reply, before NAT | 198.51.100.20:443 | 203.0.113.1:40001 |
| Reply, after NAT | 198.51.100.20:443 | 192.168.1.10:51234 |
The table entry is 192.168.1.10:51234 <-> 203.0.113.1:40001. The reply is accepted only because the entry exists. A packet from the internet with no matching entry has nowhere to go and is dropped. That is why NAT blocks unsolicited inbound traffic, although the real protection comes from the stateful tracking, not from address hiding.
On Linux the table is the connection tracker:
# List tracked connections (needs the conntrack tool)sudo conntrack -L | head -3# tcp 6 431999 ESTABLISHED src=192.168.1.10 dst=198.51.100.20 sport=51234 dport=443 \#   src=198.51.100.20 dst=203.0.113.1 sport=443 dport=40001 [ASSURED]
# How full is it?sysctl net.netfilter.nf_conntrack_count net.netfilter.nf_conntrack_max# A full table shows up in the kernel log as: nf_conntrack: table full, dropping packet
Costs of NAT
Section titled “Costs of NAT”- Port exhaustion. A public IP has about 64,000 usable ports per destination. A busy service behind a NAT gateway that opens many connections to one destination can run out. Cloud NAT gateways expose this as an error counter, such as
ErrorPortAllocationon AWS. Fix it by adding public IPs, reusing connections, or spreading destinations. - No inbound connections. Hosts behind NAT cannot accept unsolicited connections without a port forward. Peer-to-peer and voice applications use STUN, TURN, and ICE to work around this.
- Protocols that carry addresses in the payload, such as active-mode FTP and SIP, break unless the NAT device rewrites the payload (an application layer gateway).
- It blurs layering. A router rewrites transport ports, which are meant to identify processes, not hosts. See the end-to-end discussion in Introduction to networking.
Carrier-grade NAT
Section titled “Carrier-grade NAT”ISPs short of IPv4 addresses put a second NAT in their own network. Many subscribers share one public address, and each subscriber’s home router receives an address from 100.64.0.0/10 on its WAN side. If ip addr or the router’s status page shows a 100.64.x.x WAN address, port forwarding cannot work, because the inbound connection never reaches you. Shared public IPs also mean shared reputation: one abusive neighbor can get the address rate-limited or blocked. The fixes are an IPv6 path, a request for a public IP from the ISP, or an outbound tunnel to a relay you control.
See Firewall rules and iptables for iptables chains and connection-tracking rules.
VPNs - Virtual Private Networks
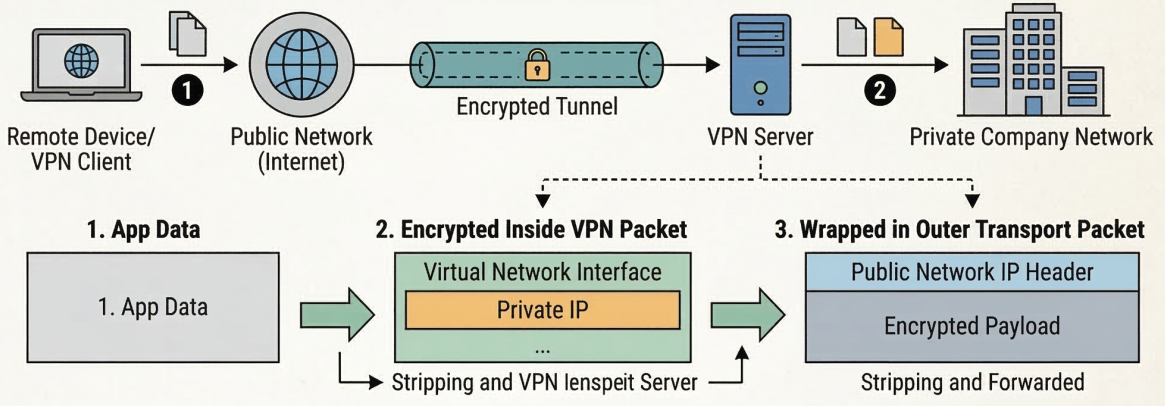
Section titled “VPNs - Virtual Private Networks”A VPN creates an encrypted tunnel over a public network (the internet), making it appear as if remote devices are on the same local network.
How VPN Tunneling Works
Section titled “How VPN Tunneling Works”- VPN client establishes an encrypted connection to the VPN server
- Client gets a virtual network interface with an IP from the company’s private address space
- Application data is encrypted and wrapped inside the transport layer payload of regular packets
- At the VPN server, the outer packet is stripped, the payload is decrypted, and the inner packet is forwarded onto the private network
Site-to-site VPN - connects two entire networks (office A to office B) so all devices on both networks can communicate as if they were local. The VPN runs between routers/firewalls, transparent to end users.
Proxy Services
Section titled “Proxy Services”A proxy is an intermediary that sits between a client and a server. The client talks to the proxy, and the proxy talks to the server on the client’s behalf.
Proxy Types
Section titled “Proxy Types”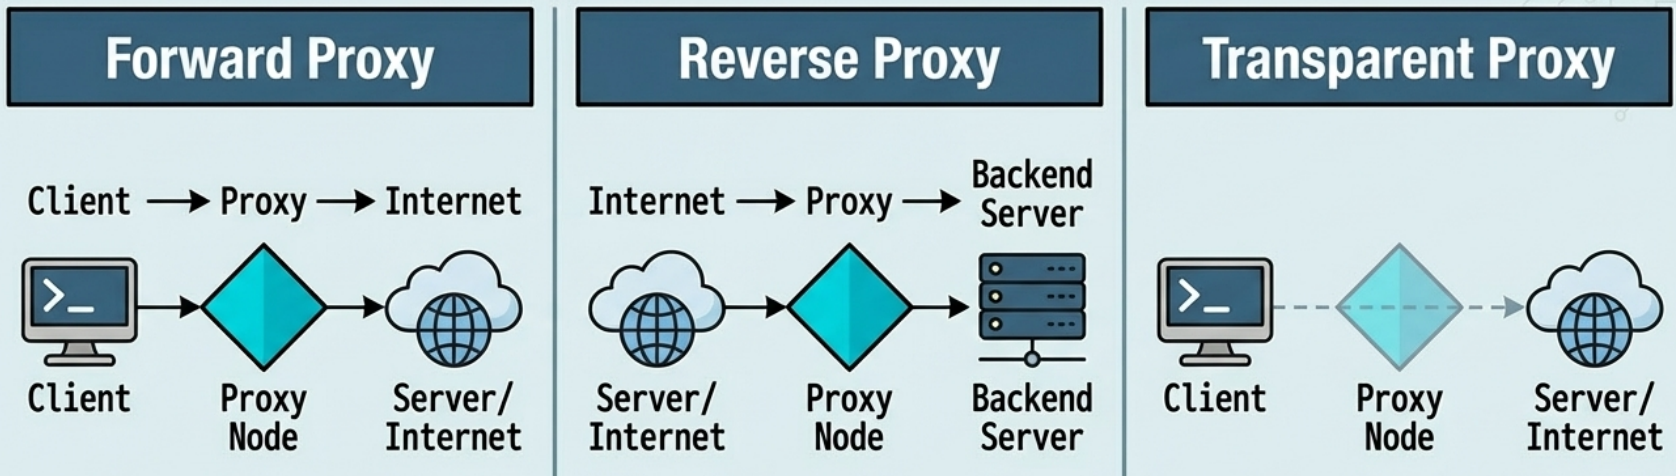
| Type | Direction | Use Case |
|---|---|---|
| Forward proxy | Client -> Proxy -> Internet | Anonymity, content filtering, corporate access control, caching |
| Reverse proxy | Internet -> Proxy -> Backend servers | Load balancing, SSL termination, caching, DDoS protection |
| Transparent proxy | Invisible to client (network-level intercept) | ISP content filtering, corporate monitoring |
Forward proxy - historically used for caching (save bandwidth by serving cached copies of frequently accessed pages). Today mostly used for content filtering and access control in corporate networks.
Reverse proxy - the client thinks it’s talking to one server, but the proxy distributes requests across multiple backend servers. Also handles TLS termination (offloading encryption from backend servers). Examples: Nginx, HAProxy, Cloudflare, AWS ALB.
For encrypting and signing mail, see Email security.
Email moves between servers with SMTP and is read from a mailbox with a separate access protocol.
- User agent - the mail client or webmail interface where a person writes and reads messages.
- Mail server - holds each user’s mailbox and an outgoing queue. Every mail server also acts as an SMTP client when it sends.
- SMTP - pushes a message from one host to the next over TCP.
- Access protocol - lets a user agent pull messages from its mailbox: IMAP, POP3, or HTTP for webmail.
flowchart LR
    A["Sender's client"] -->|"SMTP submission"| B["Sender's mail server"]
    B -->|"SMTP, port 25"| C["Recipient's mail server"]
    C -->|"IMAP or HTTP"| D["Recipient's client"]
The sender’s client does not deliver straight to the recipient’s server because a client is often offline or behind NAT. It hands the message to its own always-on server, which finds the destination by looking up the MX record for the recipient’s domain and connects to the lowest-preference server that answers. If that server is down, the message stays in the queue and the sender’s server retries, typically for several days, before it returns a bounce.
dig MX example.com +short# 10 mail1.example.com.# 20 mail2.example.com.SMTP conversation
Section titled “SMTP conversation”SMTP is a short text dialogue. A client announces itself, names the sender and recipients, sends the message, and quits. Every server reply starts with a three-digit status code: 2xx means success, 3xx means “continue”, 4xx is a temporary failure, and 5xx is permanent.
# Submission with STARTTLS on port 587 (port 25 is often blocked outbound by providers)openssl s_client -starttls smtp -crlf -connect mail.example.com:587S: 220 mail.example.com ESMTP readyC: EHLO client.example.orgS: 250 STARTTLSC: MAIL FROM:<[email protected]>S: 250 OKC: RCPT TO:<[email protected]>S: 250 OKC: DATAS: 354 End data with <CR><LF>.<CR><LF>C: Subject: testC:C: Hello.C: .S: 250 QueuedC: QUITS: 221 ByeMAIL FROM and RCPT TO form the envelope, which servers use for routing and for bounces. The From: and To: lines inside the message are separate headers shown to the reader, and they don’t have to match the envelope. That gap is what spoofing exploits, and it is why SPF checks the envelope sender, DKIM signs the headers and body, and DMARC ties the result to the visible From: domain. See Social engineering attacks for those controls.
SMTP was designed for 7-bit ASCII text. Attachments and non-ASCII text are encoded with MIME (usually base64) before sending and decoded on arrival, which makes a message about a third larger than its raw content.
Reading mail
Section titled “Reading mail”| Protocol | Port (TLS) | Behavior |
|---|---|---|
| IMAP | 993 | Messages and folders stay on the server. Several devices see the same state |
| POP3 | 995 | Downloads messages to one device, normally deleting them from the server |
| HTTP | 443 | Webmail and mobile apps talk to the provider’s web interface |
Troubleshooting
Section titled “Troubleshooting”| Symptom | Likely cause | Fix |
|---|---|---|
| Mail delayed, not bounced | Recipient server unreachable, sender is retrying | Check the queue, then test reachability with nc -zv mail1.example.com 25 |
| Connection to port 25 times out from a cloud host | Provider blocks outbound port 25 | Send through an authenticated relay on port 587 |
Mail lands in spam or is rejected with a 550 | Missing or failing SPF, DKIM, or DMARC | Publish the DNS records and check the sender alignment |
User unknown bounce for a valid user | MX points to a server that doesn’t host that mailbox | Check dig MX and the priority order |