
Troubleshooting and the Future of Networking
Troubleshooting Fundamentals
Section titled “Troubleshooting Fundamentals”Network issues can occur at any layer of the stack. Effective troubleshooting means systematically isolating which layer is broken:
| Layer | What to check | Tool |
|---|---|---|
| Physical (L1) | Cable connected? Link light on? | Visual inspection, cable tester |
| Data Link (L2) | MAC address resolving? Switch port up? | ip link, ethtool, ARP table |
| Network (L3) | Can you reach the IP? Route exists? | ping, traceroute, ip route |
| Transport (L4) | Is the port open? Connection established? | nc, ss, telnet, tcpdump |
| Application (L5) | Is the service responding correctly? | curl, dig, openssl s_client |
ICMP and the ping Command
Section titled “ICMP and the ping Command”ICMP (Internet Control Message Protocol) is the “error reporting” protocol of the network layer. When something goes wrong with IP packet delivery, routers send ICMP messages back to the source.
ICMP Packet Structure
Section titled “ICMP Packet Structure”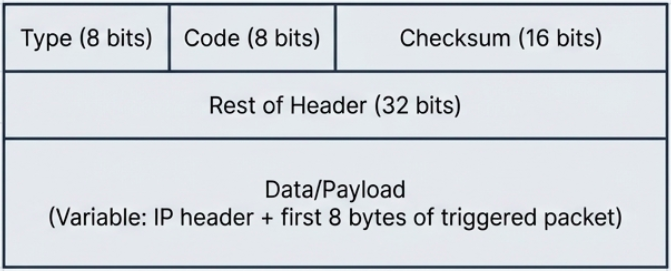
| Field | Size | Purpose |
|---|---|---|
| Type | 8 bits | What kind of ICMP message (see table below) |
| Code | 8 bits | Subtype within the message type |
| Checksum | 16 bits | Integrity check for the ICMP header + data |
| Rest of Header | 32 bits | Varies by type (e.g., sequence number for echo) |
| Data/Payload | Variable | Contains the IP header + first 8 bytes of the packet that triggered the error |
Common ICMP Types
Section titled “Common ICMP Types”| Type | Code | Meaning |
|---|---|---|
| 0 | 0 | Echo Reply (response to ping) |
| 3 | 0 | Destination network unreachable |
| 3 | 1 | Destination host unreachable |
| 3 | 2 | Destination protocol unreachable |
| 3 | 3 | Destination port unreachable |
| 3 | 4 | Fragmentation needed but DF set (path MTU discovery) |
| 3 | 13 | Communication administratively prohibited (firewall) |
| 5 | 0 | Redirect: a better first hop exists |
| 8 | 0 | Echo Request (outgoing ping) |
| 11 | 0 | TTL exceeded (used by traceroute) |
| 12 | 0 | Bad IP header |
ICMP messages travel inside IP datagrams as protocol 1. Source Quench (type 4) was once a congestion signal and is obsolete. The ping reply is generated by the operating system kernel, with no application involved, so a fast ping does not prove that a service is healthy. IPv6 uses ICMPv6 (RFC 4443), which adds Packet Too Big and the Neighbor Discovery messages. See IPv6.
ping in Practice
Section titled “ping in Practice”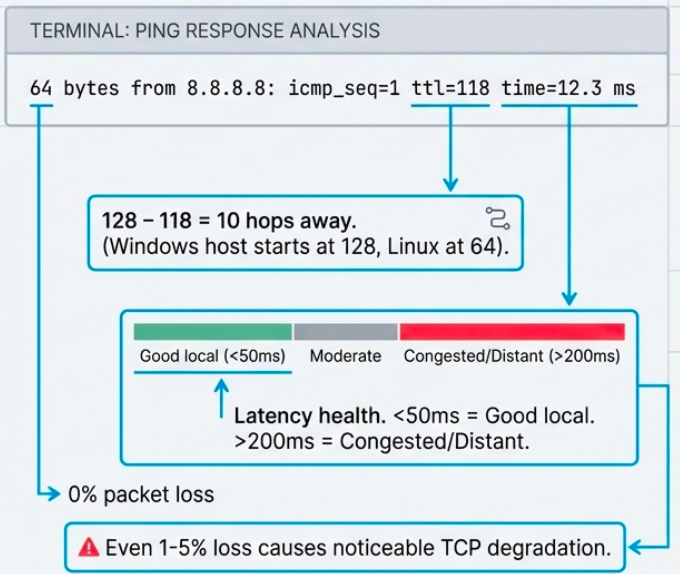
# Basic connectivity test (Linux - 4 packets)ping -c 4 8.8.8.8# PING 8.8.8.8 (8.8.8.8) 56(84) bytes of data.# 64 bytes from 8.8.8.8: icmp_seq=1 ttl=118 time=12.3 ms# 64 bytes from 8.8.8.8: icmp_seq=2 ttl=118 time=11.8 ms# --- 8.8.8.8 ping statistics ---# 4 packets transmitted, 4 received, 0% packet loss, time 3004ms# rtt min/avg/max/mdev = 11.8/12.1/12.3/0.2 ms
# Ping a hostname (tests DNS + connectivity)ping -c 4 google.com
# Continuous ping (stop with Ctrl+C)ping google.com
# Ping with specific packet size (test MTU)ping -c 4 -s 1472 -M do 192.168.1.1# -s 1472 = payload size (1472 + 28 overhead = 1500 MTU)# -M do = don't fragment flag# If "Frag needed" appears, MTU is smaller than expected
# Windows equivalentping -n 4 8.8.8.8ping -t 8.8.8.8 # continuous (Ctrl+C to stop)Traceroute
Section titled “Traceroute”Traceroute maps the path packets take from you to a destination by exploiting TTL behavior. It sends packets with incrementally increasing TTLs (1, 2, 3…), causing each router along the path to send back an ICMP “Time Exceeded” message.
Each TTL value is sent three times, which is why every hop shows three timings. The source needs a signal to stop. The default probe is a UDP datagram to an unlikely high port. Each router on the way returns ICMP type 11 (TTL exceeded). The destination has no process on that port, so it returns type 3 code 3 (port unreachable), and the trace ends. Other probe types end differently:
| Probe | Option | Hops answer with | Destination answers with |
|---|---|---|---|
| UDP to a high port | default | Type 11 | Type 3 code 3 |
| ICMP echo | -I | Type 11 | Echo reply |
| TCP SYN | -T -p 443 | Type 11 | SYN-ACK or RST |
Use TCP probes when a firewall drops UDP and ICMP but allows the service port.
# Linux/Mac - uses UDP probes by defaulttraceroute google.com#  1  gateway (192.168.1.1)  1.234 ms  0.987 ms  1.123 ms#  2  isp-router (10.0.0.1)  5.678 ms  4.321 ms  5.123 ms#  3  * * *                                                     # no response (firewall)#  4  72.14.236.208  12.345 ms  11.234 ms  12.678 ms#  5  google-dns (8.8.8.8)  13.456 ms  12.789 ms  13.234 ms
# TCP traceroute (bypasses ICMP-blocking firewalls)sudo traceroute -T -p 443 example.com
# mtr - combines ping + traceroute in real-time (best tool for diagnosing path issues)mtr google.com# Shows live updating statistics: loss%, sent, last RTT, avg, best, worst
# mtr as a single report (useful for sharing)mtr --report --report-cycles 10 google.com
# Windowstracert google.com # uses ICMP echo by defaultpathping google.com # longer-running trace with statistics per hopTesting Port Connectivity
Section titled “Testing Port Connectivity”When ping (L3) works but a service is unreachable, the issue is likely at the transport layer (L4). Test specific ports:
# netcat (nc) - the Swiss Army knife of networking# Test if a TCP port is open (Linux/Mac)nc -zv example.com 443# Connection to example.com (93.184.216.34) 443 port [tcp/https] succeeded!# -z = scan mode (don't send data)# -v = verbose
# Scan a range of portsnc -zv 192.168.1.1 20-25 80 443
# Test UDP port (harder - may not get a response even if open)nc -zuv 8.8.8.8 53
# Windows equivalentTest-NetConnection -ComputerName example.com -Port 443# ComputerName     : example.com# RemotePort       : 443# InterfaceAlias   : Ethernet# TcpTestSucceeded : True
# Quick multi-port check with bash loopfor port in 22 80 443 3306 5432 8080; do nc -zv myserver.com $port 2>&1 | grep -E "succeeded|refused"doneDNS Troubleshooting
Section titled “DNS Troubleshooting”dig - The Practitioner’s DNS Tool
Section titled “dig - The Practitioner’s DNS Tool”dig (Domain Information Groper) replaced nslookup as the go-to DNS debugging tool on Linux/Mac. It shows the full DNS response including answer section, authority section, and timing.
# Basic lookupdig example.com# ;; ANSWER SECTION:# example.com.    3600  IN  A  93.184.216.34# ;; Query time: 23 msec# ;; SERVER: 127.0.0.53#53(127.0.0.53)
# Short output (just the answer)dig +short example.com# 93.184.216.34
# Query specific record typesdig MX gmail.com           # mail serversdig NS example.com         # nameserversdig TXT example.com        # SPF, DKIM, verificationdig AAAA example.com       # IPv6 addressdig -x 8.8.8.8             # reverse lookup (IP -> name)
# Query a specific DNS serverdig @8.8.8.8 example.comdig @1.1.1.1 example.com
# Trace the full resolution path (root -> TLD -> authoritative)dig +trace example.com
# Check if DNS propagation is complete (compare servers)dig @8.8.8.8 example.com +shortdig @1.1.1.1 example.com +shortdig @ns1.example.com example.com +short
nslookup - Cross-Platform Alternative
Section titled “nslookup - Cross-Platform Alternative”# Basic lookupnslookup example.com
# Query a specific servernslookup example.com 8.8.8.8
# Interactive modenslookup> server 8.8.8.8 # switch DNS server> set type=MX # change record type> gmail.com # query> set debug # show full response packets> exit
# Specific record type (non-interactive)nslookup -type=MX gmail.comnslookup -type=NS example.comDNS Registration
Section titled “DNS Registration”- ICANN sits at the top of the DNS hierarchy, managing the root zone
- Registrars (GoDaddy, Namecheap, Cloudflare, etc.) sell domain names under agreements with ICANN
- Domain transfers between registrars require verification through a special TXT or authorization code
- Domains have expiration dates - if you forget to renew, the domain can be purchased by anyone (domain squatting)
The Hosts File
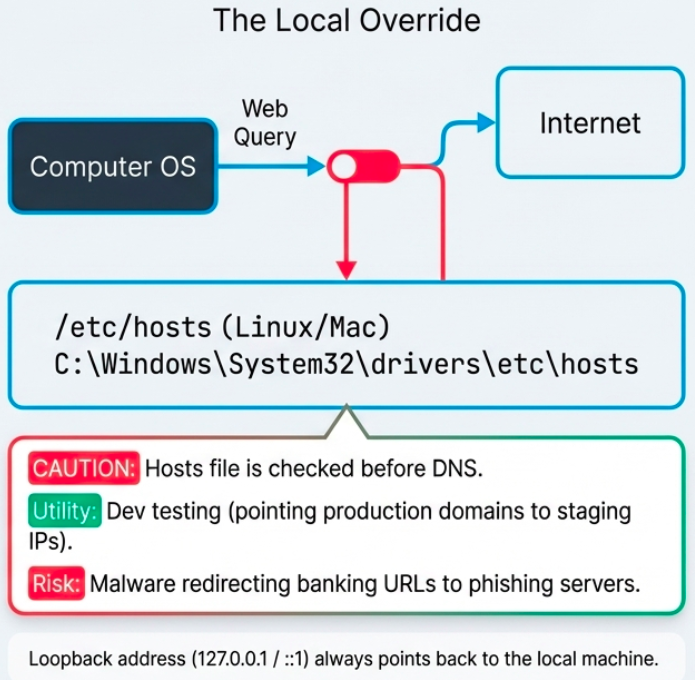
Section titled “The Hosts File”Before DNS existed, all name-to-IP mappings lived in a single flat file - the hosts file. It still exists on every OS:
| OS | Path |
|---|---|
| Linux / Mac | /etc/hosts |
| Windows | C:\Windows\System32\drivers\etc\hosts |
# Hosts file format (IP followed by hostname)127.0.0.1 localhost::1 localhost192.168.1.50 myserver.local10.0.0.5 staging.example.com # override DNS for testingThe loopback address (127.0.0.1 for IPv4, ::1 for IPv6) always points back to the local machine. Used for local development servers and testing without touching the network.
Cloud Computing Models
Section titled “Cloud Computing Models”Cloud computing delivers IT resources over the internet with pay-as-you-go pricing. The underlying technology is hardware virtualization - a hypervisor runs multiple virtual machines on shared physical hardware.
Cloud Deployment Models
Section titled “Cloud Deployment Models”| Model | Who owns it | Accessed by | Pros | Cons |
|---|---|---|---|---|
| Public | Third-party provider (AWS, GCP, Azure) | Anyone over internet | Scalable, cheap, no hardware maintenance | Shared infrastructure, less control |
| Private | Your organization | Internal only | Full control, security, compliance | Expensive, requires own staff |
| Hybrid | Mix of both | Depends on workload | Flexible, keep sensitive data private | Complex to manage |
Cloud Service Models
Section titled “Cloud Service Models”| Model | You manage | Provider manages | Example |
|---|---|---|---|
| IaaS (Infrastructure) | OS, apps, data | Hardware, networking, virtualization | AWS EC2, GCP Compute Engine |
| PaaS (Platform) | Apps, data | OS, runtime, hardware | Heroku, Google App Engine, Azure App Service |
| SaaS (Software) | Just use it | Everything | Gmail, Slack, Salesforce |
IPv6 addressing, the header, SLAAC and Neighbor Discovery, and the IPv4 transition methods are covered in IPv6. For troubleshooting, use the -6 flag on ping, traceroute, mtr, and curl, and do not filter ICMPv6.